Category: Security
-
Read more: Modern password tips based on NIST guidelines
Passwords are an inherently flawed security measure in an era of constant phishing attacks and massive data leaks. This guide breaks down the latest recommendations from the National Institute of…
-
Zero trust in practice: Implementing a zero trust security model for mid-sized enterprises
Read more: Zero trust in practice: Implementing a zero trust security model for mid-sized enterprisesIn modern business, evolving IT environments require you to shift the way you approach data protection. A zero trust security model fundamentally changes the rules by assuming threats already exist…
-
Cybersecurity and resilience: Building a culture of preparedness
Read more: Cybersecurity and resilience: Building a culture of preparednessWith businesses under constant risk of attack and disruption from complex and evolving threats, it’s imperative to develop not only a cybersecurity system but also a cyber resilience plan to…
-
Not all hackers are criminals: A look at the three major hacker types
Read more: Not all hackers are criminals: A look at the three major hacker typesWhile the term “hacker” often dominates cybersecurity conversations, it’s crucial to recognize that not all hackers share the same motivations. Some exploit vulnerabilities, others help organizations fix them, and some…
-
IT security compliance as a competitive edge: Turning regulatory burdens into market wins
Read more: IT security compliance as a competitive edge: Turning regulatory burdens into market winsMost business leaders view regulatory requirements as a grudge purchase — a necessary tax on doing business that drains resources and distracts from revenue-generating work. However, in a market where…
-
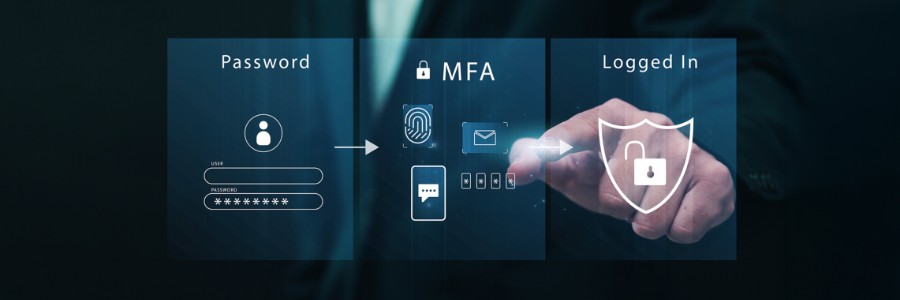
The hidden weaknesses of multifactor authentication
Read more: The hidden weaknesses of multifactor authenticationMultifactor authentication (MFA) works by requiring users to provide more than one form of identification when logging into a system or account. This extra layer of security is meant to…
-
The boardroom language of risk: How to translate cyberthreats into cybersecurity ROI
Read more: The boardroom language of risk: How to translate cyberthreats into cybersecurity ROIPicture a CISO presenting a heat map of thwarted attacks to the board. The directors stare at the screen, attempting to make sense of the colors, before asking the only…
-
2026 Cybersecurity trends and predictions
Read more: 2026 Cybersecurity trends and predictionsCybersecurity experts Rob Wright (Dark Reading), David Jones (Cybersecurity Dive), and Alissa Irei (TechTarget Search Security) recently came together to discuss the future of online security. Let’s take a look…
-
Tips for creating more secure business passwords
Read more: Tips for creating more secure business passwordsStrong passwords are one of the easiest and most effective ways to protect online accounts. Still, many businesses use weak or reuse credentials. Learning how to create stronger passwords can…
-
Enterprise cyber security solutions: Why your business needs a proactive cyber resilience strategy, not just tools
Read more: Enterprise cyber security solutions: Why your business needs a proactive cyber resilience strategy, not just toolsYour enterprise has invested heavily in security. You have the best firewalls, advanced endpoint security to protect devices, and even premium Microsoft E5 licenses that go far beyond basic antivirus…